AI는 이제 코딩의 진입장벽을 거의 없애고 있지만, ‘작동하는 앱’과 ‘안전한 앱’을 만드는 능력은 아직 같은 수준이 아니다.
특히, 딸깍앱이 기업 데이터, 개인정보, 결제, 업무시스템과 연결되는 순간, 개발 문제가 아니라 사이버보안, 개인정보보호, Shadow IT 문제가 된다.
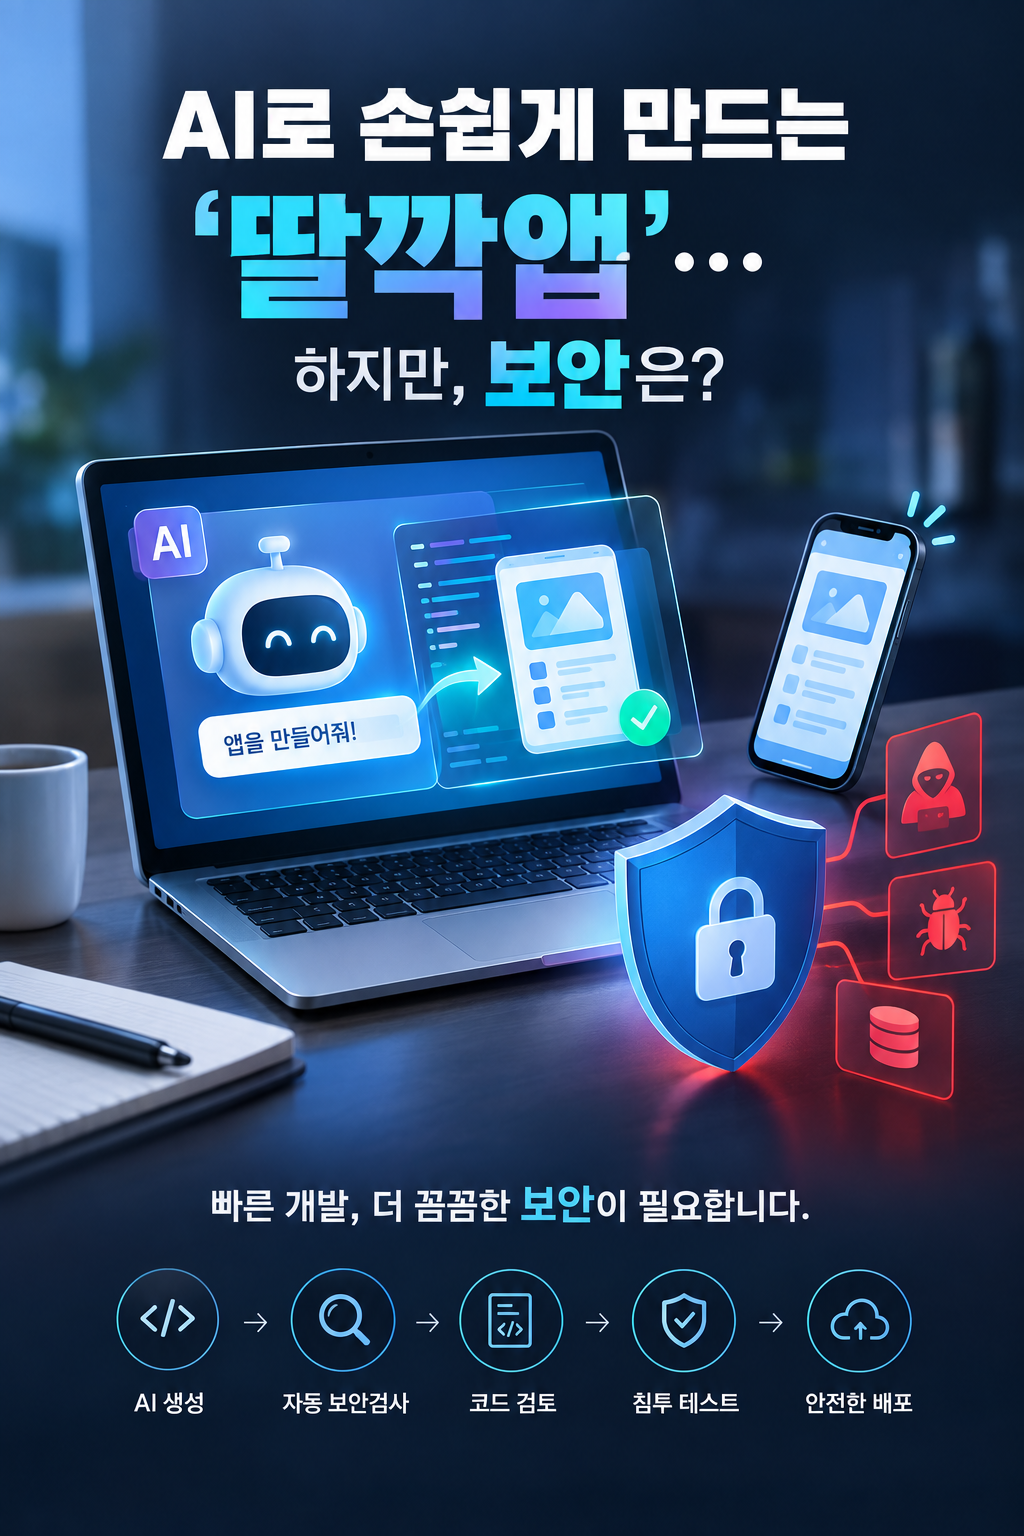
따라서, 앞으로는 ‘AI로 빠르게 만드는 능력’보다 AI 생성물에 대한 자동 보안검사, 권한통제, 코드검토, 침투테스트를 기본값으로 만드는 ‘AI Secure Development’ 체계가 중요해진다.
- ‘딸깍앱’ = 바이브 코딩(Vibe Coding)
o 자연어로 원하는 기능을 설명하면 AI가 코드 작성 → 수정 → 앱 제작까지 수행
o 비개발자도 짧은 시간에 앱을 만들 수 있어 개발 진입장벽이 크게 낮아짐. - 문제는 ‘작동’과 ‘보안’이 별개라는 것
- AI가 생성한 코드 자체에도 보안 취약점이 반복
o Veracode의 2026년 연구에서는 AI 코드 생성 작업의 약 44%가 알려진 보안 취약점을 포함한 것으로 나타남.
o 2025년 연구에서도 약 45%가 OWASP Top 10 관련 보안 테스트를 통과하지 못함. - 특히 반복되는 취약점
o 인증·권한관리 미흡
o 관리자 권한 우회
o API Key·비밀번호 등 Secret 노출
o SQL Injection
o 입력값 검증 부족
o 데이터베이스 접근제어 미흡
o Rate Limiting 부재
o 개인정보·민감정보 노출
o 잘못된 CORS·보안 설정 등. - ‘기능을 추가할수록’ 보안 문제가 생길 수 있음
- AI에게 “보안을 고려해 만들어 달라”고 하는 것만으로도 개선 가능하지만 충분하지 않음
- OWASP도 ‘AI 생성 코드에 대한 부적절한 신뢰’를 별도 위험으로 지적 : AI가 만든 코드를 사람이 이해·검토하지 않고 그대로 사용하는 것이 핵심 위험으로 제시됨.
- 기업에서는 ‘Shadow AI’ 문제가 확대될 가능성
o 직원이 AI로 만든 앱을 회사 데이터베이스와 연결하고 외부에 공개하면 IT부서가 모르는 비공식 업무 시스템이 생길 수 있음.
o 2026년 RedAccess 조사에서는 수십만 개의 공개 자산 중 민감한 기업정보가 노출된 사례가 보고됨. - 따라서 핵심은 ‘AI를 쓰지 말라’가 아님 : 대신 AI 생성 → 자동 보안검사 → 코드/구조 검토 → 침투테스트 → 배포라는 보안 게이트가 필요함.
[1]: https://v.daum.net/v/20260908075852899 "AI로 손쉽게 만드는 ‘딸깍앱’…보안은?"
[2]: https://faq.donga.com/NEWS/It/article/all/20260220/133387103/1 "코딩 몰라도 앱 만든다고? 바이브 코딩, 직접 해보니|동아일보"
[3]: https://view.ceros.com/veracode/genai-code-security-report2026 "2026 - GenAI Code Security Report 2026"
[4]: https://www.veracode.com/blog/genai-code-security-report/ "Insights from 2025 GenAI Code Security Report"
[5]: https://securityboulevard.com/2026/05/5-vulnerabilities-in-every-vibe-coded-app/ "5 Vulnerabilities in Every Vibe-Coded App - Security Boulevard"
[6]: https://arxiv.org/abs/2608.20963 "Vibe Coding and Web Application Security: A Twin-Prompt Study"
[7]: https://top10.owasp.org/2025/ko/X01_2025-Next_Steps/ "다음 단계 - OWASP Top 10:2025"
[8]: https://venturebeat.com/security/vibe-coded-apps-shadow-ai-s3-bucket-crisis-ciso-audit-framework "5,000 vibe-coded apps just proved shadow AI is the new S3 bucket crisis | VentureBeat"
[9]: https://www.veracode.com/blog/spring-2026-genai-code-security/ "Spring 2026 GenAI Code Security Update"
[10]: https://www.etoday.co.kr/news/view/2482887 "AI가 개발하는 시대…전세계 ‘바이브코딩’ 열풍 - 이투데이"
[11]: https://news.nate.com/view/20260423n25839 "바이브 코딩 넘어 '바이브 해킹' 진입…미소스 이후 보안은 : 네이트 뉴스"
[12]: https://kaoes.or.kr/manage/upload/0007/20260422_76476478.pdf "제7호
2026년 4월
물-에너지 넥서스, 지속가능한 미래를 위한 선택
Data Cen"
[13]: https://www.cloudflare.com/ko-kr/learning/ai/ai-vibe-coding/ "바이브 코딩 뜻과 LLM 코딩 보안 | Cloudflare"
[14]: https://www.ibm.com/kr-ko/think/topics/vibe-coding "Vibe 코딩이란 무엇인가? | IBM"
[15]: https://www.invicti.com/blog/security-labs/security-issues-in-vibe-coded-web-apps-analyzed "Security Issues in Vibe-Coded Web Apps: Analysis, Vulnerabilities, Scanning"
[16]: https://www.securityweek.com/vibe-coded-apps-riddled-with-exploitable-security-flaws/amp/ "Vibe-Coded Apps Riddled With Exploitable Security Flaws - SecurityWeek"
[17]: https://www.theverge.com/ai-artificial-intelligence/950844/vibe-coding-security-risks-apps "Read this before you vibe-code another app"
[18]: https://techcrunch.com/2025/09/14/vibe-coding-has-turned-senior-devs-into-ai-babysitters-but-they-say-its-worth-it/ "Vibe coding has turned senior devs into ‘AI babysitters,’ but they say it’s worth it | TechCrunch"
[19]: https://techcrunch.com/2025/09/28/wiz-chief-technologist-ami-luttwak-on-how-ai-is-transforming-cyberattacks/ "Wiz chief technologist Ami Luttwak on how AI is transforming cyberattacks | TechCrunch"
[20]: https://techcrunch.com/podcast/vibe-coding-meet-vibe-security/ "Vibe coding? Meet vibe security | TechCrunch"
[21]: https://arstechnica.com/ai/2026/08/cloudflare-open-sources-vibe-coding-platform-for-people-who-arent-coders/?utm_source=chatgpt.com "Cloudflare open-sources vibe-coding platform for people who aren't coders - Ars Technica"
[22]: https://arstechnica.com/security/2026/05/fed-up-with-vibe-coders-dev-sneaks-data-nuking-prompt-injection-into-their-code/?bxid=641db5c897cd3705180410e2&cndid=73329705&esrc=&hasha=26ee562944d70e222486825611137fcb&hashb=d046955a4eedd62fc9609cb0c04171bd891c1228&hashc=ef9cb8d3bbeb2fa82ec56a45e40545c130fa8256a9d7de6ca174be6ed11b173a "Fed up with vibe coders, dev sneaks data-nuking prompt injection into their code - Ars Technica"
[23]: https://www.theregister.com/software/2026/01/22/ai-vibe-coding-automation-convenience-and-security-debt/4721210 "AI vibe coding: automation convenience and security debt"
[24]: https://www.theregister.com/software/2026/01/08/yes-criminals-are-using-ai-to-vibe-code-malware/4205713 "Yes, criminals are using AI to vibe-code malware"
[25]: https://www.theregister.com/security/2026/04/21/lovable-denies-data-leak-cites-intentional-behavior/5226233?td=keepreading "Lovable denies data leak, cites 'intentional behavior'"
[26]: https://venturebeat.com/infrastructure/vercel-rebuilt-v0-to-tackle-the-90-problem-connecting-ai-generated-code-to "Vercel rebuilt v0 to tackle the 90% problem: Connecting AI-generated code to existing production infrastructure, not prototypes | VentureBeat"
[27]: https://www.nowsecure.com/blog/2026/04/07/ai-vibe-coding-for-mobile-apps-easy-or-secure/ "Mobile App Security Risks in AI Vibe Coded Apps - NowSecure"
[28]: https://arxiv.org/abs/2512.03262 "Is Vibe Coding Safe? Benchmarking Vulnerability of Agent-Generated Code in Real-World Tasks"
'인공지능 관련 뉴스@기사' 카테고리의 다른 글
| 메타, 예약 소핑 결제까지 Muse (0) | 2026.09.23 |
|---|---|
| GPT-6 Astra와 반도체 슈퍼사이클 (0) | 2026.09.22 |
| 가트너, AI 전사 확장 성공 기업은 22%에 불과 (0) | 2026.09.22 |
| 뉴욕, 초중생 학교내 AI 사용금지 (0) | 2026.09.22 |
| 오플클로, AI가 직접 실행하는 에이전트 시대 (0) | 2026.09.21 |


